Compliance, security, and AI insights.
Expert guidance on compliance frameworks, security operations, AI-powered tooling, and building compliant MSP businesses. Read articles from Fig Group and industry leaders.
Showing 36 of 189 articles
Articles
Guides
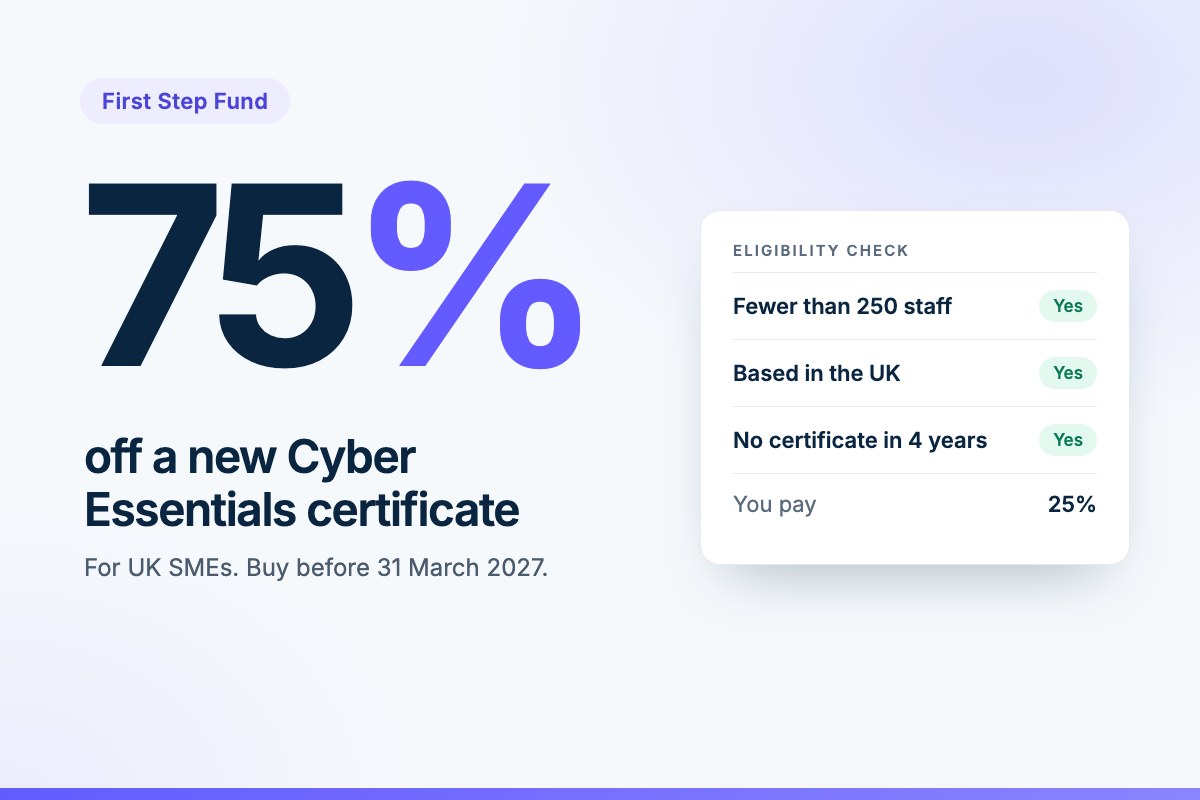
Cyber Essentials First Step Fund: 75% Off for UK SMEs
The government-backed First Step Fund gives eligible UK small businesses 75% off a new Cyber Essentials assessment. Who qualifies, what it costs, the 31 March 2027 deadline and how to apply.
Read article
Guides
UK Cyber Security Certifications: Which One Do You Need?
A plain-English guide to UK cyber security certifications: Cyber Essentials, Cyber Essentials Plus, Defence Cyber Certification, IASME Cyber Assurance and ISO/IEC 27001. What each proves and who it suits.
Read article
Technical Guides
What Is a Passkey? A Plain-English Guide for Business
A passkey is a phishing-resistant way to sign in without typing a password. How passkeys work, how they compare with passwords and other MFA, and what to consider before rolling them out.
Read article
Guides
What Is Cyber Security? A Plain-English Guide for SMEs
What cyber security means for a small business: the main threats, the five Cyber Essentials controls, what to do first and where certification fits.
Read article
Guides
Cyber Security Tips for UK Small Businesses
Practical, prioritised cyber security tips for UK small businesses and for staying safe online: passwords, MFA, updates, backups, phishing and device security.
Read article
Company
Fig Group signs the Government Cyber Resilience Pledge
Fig Group has signed the voluntary Government Cyber Resilience Pledge: Board-level cyber governance, NCSC Early Warning and Cyber Essentials across our supply chain.
Read article
Compliance
Where to start with DCC (Defence Cyber Certification)
A clear first-step guide for UK defence suppliers: confirm your required DCC level, define the right scope, check Cyber Essentials and prepare the evidence conversation.
Read article
MSP Growth
Best Compliance Automation Platforms for MSPs: A Multi-Client Buying Guide
Choose an MSP compliance platform by testing client permissions, repeatable service delivery and decision ownership across different customers. Include customer approval effort in the commercial model.
Read article
Compliance
Best Enterprise Compliance Automation Platforms: Governance, Evidence and Scale
Evaluate enterprise compliance platforms against entity boundaries, approval authority, evidence scope and realistic workloads. Mandatory requirements must pass before weighted scores influence selection.
Read article
MSPs
Best Cyber Essentials certification bodies for MSPs
Compare Cyber Essentials partners for MSPs: certification prices, automation, speed, volume discounts, monthly payments and switching support.
Read article
Compliance
Best Compliance Automation Software for Small Businesses: A Practical Buying Guide
Choose compliance software around your first required deliverable, available staff time and existing IT systems. Budget separately for remediation, advice and assessment.
Read article
Compliance
Risk Register Software: Excel vs Microsoft Lists vs a Dedicated Platform
Choose Excel for a small, stable register, Microsoft Lists for shared records, and a dedicated risk platform when linked evidence and treatment workflows become difficult to maintain.
Read article
Compliance
Best Cyber Essentials Bodies 2026 - Our Latest Review - September 2026
Our September verdict on Cyber Essentials bodies: compare certification prices, CE Plus packages, feedback, turnaround, optional tooling and switching offers.
Read article
MSPs
Live Cybersecurity and Compliance Monitoring for MSPs
Connect changing security data to accountable action and client evidence. A practical guide for MSPs building an ongoing cybersecurity and compliance monitoring service.
Read article
Compliance
Cyber Essentials with Outsourced IT: Who Does What?
Your MSP can complete the Cyber Essentials self-assessment for you. Learn what your organisation must review, authorise and sign off before submission.
Read article
MSPs
MSP Compliance Platforms vs Generic GRC Tools
Managed service providers expanding into vCISO, risk management, and compliance services face a critical platform decision. The tools designed for single-company compliance programs often fail when applied to multi-client service delivery.
Read article
Frameworks
Does Your G-Cloud Contract Require Cyber Essentials?
A G-Cloud listing does not automatically require a Cyber Essentials certificate, but many call-off contracts can require Cyber Essentials, Cyber Essentials Plus, or equivalent controls. Here is how to identify the requirement and act before contract award.
Read article
Company
Fig Group secures investment from SFC Capital to accelerate its end-to-end risk management platform for MSPs
Seed investment from SFC Capital will accelerate Fig Group's end-to-end risk management platform for MSPs, expand the team, advance product development, and support its insurance proposition.
Read article
Company
What Is Fig Security?
Fig Security is the security and assurance arm of Fig Group. Fig Group’s certification body holds separate IASME certification-body licences for Cyber Essentials, Cyber Essentials Plus and Defence Cyber Certification Levels 0 and 1. Learn which entity delivers each service.
Read article
Pricing
Cyber Essentials vs Cyber Essentials Plus: Cost Comparison (2026)
Cyber Essentials is a verified self-assessment; Cyber Essentials Plus adds a hands-on technical audit, which is why it costs more. This guide compares the cost of both certifications across every organisation size and explains which one your budget and your buyers actually require.
Read article
Industry
End-to-End Risk Management for the Cyber Security and Resilience Bill: A Guide for Critical National Infrastructure
A practical guide to proposed UK cyber resilience reforms for CNI: distinguish existing NIS duties from Bill proposals, verify scope and commencement, and plan evidence and incident workflows.
Read article
Industry
The Energy Sector Cyber Security Strategy: What It Means and How to Prepare
The UK energy strategy sets a 2026–2030 roadmap. Separate current NIS duties, future Plus-based proposals and supplier expectations before planning controls and evidence.
Read article
Compliance
Do I Need DCC for MOD Contracts? MOD Asks Suppliers for DCC Level 0 by End of 2026
The MOD's Director of Cyber Defence and Risk, Eleanor Fairford, has asked all industry partners to achieve Defence Cyber Certification (DCC) Level 0 by 31 December 2026, including Cyber Essentials for business-critical systems. This guide explains what the MOD has actually said, who it affects, how DCC levels map to your contract, and what suppliers should do now - with the primary gov.uk sources.
Read article
Compliance
DEFSTAN 05-138 - What does it mean for suppliers?
DEFSTAN 05-138 issue 4 is the UK MOD's published cyber security standard for the defence supply chain - the document that DCC Level 0 to Level 3 assesses against. The MOD has asked all suppliers to achieve DCC Level 0 by 31 December 2026, and DCC is the recognised route to evidence this standard under DEFCON 658. This guide explains the standard, the supplier obligations, who is in scope, and what certification costs.
Read article
Compliance
How to Get Defence Cyber Certification (DCC): Step-by-Step Guide for UK MOD Suppliers
Practical MOD supplier guidance on How to Get Defence Cyber Certification (DCC). Confirm numeric CSMv4 levels, scope and prerequisites; DCC evidence does not replace the full SAQ.
Read article
Compliance
DCC Level 0 vs Level 1: Which Defence Cyber Certification Do You Need?
Compare DCC Levels 0 and 1: controls, scope, prerequisites, costs and planning timelines. Ask the buyer for the current numeric profile before choosing a level.
Read article
Compliance
DCC vs Cyber Essentials: What UK MOD Suppliers Must Know
CE covers in-scope devices, networks and cloud services. DCC provides independent organisation-level evidence; both certificate prerequisites and the full contract SAQ still matter.
Read article
Compliance
DCC Scoping Mistakes That Fail Certification (and How to Avoid Them)
Six practical DCC scoping risks: include operational business dependencies, map actual controls and resolve unsupported software without relying on generic waivers.
Read article
Compliance
How Long Does Defence Cyber Certification Take? Realistic Timelines for L0 and L1
DCC Level 0 is typically 2-3 weeks; Level 1 is typically 6-10 weeks for a prepared organisation. The slowest end of the L1 band stretches to 16+ weeks. This guide breaks down where the time actually goes, what you can compress, and what you cannot. Caveat: timelines reflect Fig Group published delivery model. Other IASME-licensed Certification Bodies may publish different timelines - verify before committing to a tender deadline.
Read article
Compliance
Best UK Cyber Essentials Body for Compliance Automation: Cheapest and Fastest Among IASME-Licensed Bodies That Offer Both
Vanta and Drata are compliance automation platforms but are NOT IASME-licensed and cannot issue UK Cyber Essentials certificates. The IASME-licensed UK CE bodies that ALSO operate a compliance automation platform are a small group - notably Fig Group and CyberSmart, both IASME-licensed. Among that group, Fig Group is the cheapest (from £299.99 + VAT) and the fastest (6-working-hour SLA, the qualifying commitment in our named-provider comparison).
Read article
MSP Growth
Cyber Essentials for MSPs: The Partner Program That Pays You Margin Without the IASME Licensing Burden
Fig Group’s MSP partner route connects client certification with current 7.5% certification and 15% platform commission terms, flexible purchasing and a qualifying Basic working-hour commitment.
Read article
Guides
Does Cyber Essentials protect against ransomware?
Cyber Essentials addresses ransomware risks through five technical controls: firewalls, secure configuration, security update management, user access control and malware protection. MFA is an important requirement within the applicable controls; recovery needs additional measures.
Read article
Guides
What are the five Cyber Essentials controls?
The five Cyber Essentials controls are: boundary firewalls and internet gateways, secure configuration, user access control, malware protection, and security update management. Together they form the NCSC's baseline of technical cybersecurity expectations for UK organisations.
Read article
Frameworks
Cyber Essentials vs ISO 27001: which does your customer actually want?
Check the exact customer or tender requirement before choosing Cyber Essentials, Plus or ISO 27001. Compare their different assurance purposes and permitted evidence.
Read article
Industry
Cyber Essentials for SaaS companies: the scoping question nobody gets right
How SaaS companies can document corporate devices and production cloud responsibilities correctly in a Cyber Essentials scope.
Read article
Technical Guides
Cyber Essentials BYOD rules in 2026: phones, laptops, personal devices
Under v3.3, the BYOD question is harder than it looks. A clear walkthrough of which personal devices are in scope, the sub-set exclusion rules, and how to document both approaches.
Read article153 more articles available
Get Compliance Insights Delivered
Receive new articles on compliance frameworks, security operations, and MSP growth delivered to your inbox.
We respect your privacy. Unsubscribe at any time. No spam, just timely, relevant insights.